Out of the dark.
Scan log · 4 paths
- 01vpn-gw.eu-westexposed
- 02legacy.portalforgotten
- 03supplier-sftpshared creds
- 04edge-fw-02unpatched
Asset register · 4 records
- SVC-014payment platformtier 1
- PRC-031change procedureowner CAB
- CTL-A.8ISO 27001 controls93 mapped
- OWN-ITremediation ownerIT ops
One organization. Two perspectives. Priorities only appear when you hold both.
Compliance is the floor, not the target.
Regulation defines the minimum. Your risk appetite defines how far cybersecurity should go beyond it. Together, they set the operating bandwidth for your security capability.
Make that boundary explicit, and cybersecurity investment becomes defensible: what you must do, what you choose to do, and which risks you accept.
Discretionary security
requirement
Set by risk appetite
Minimal compliance
requirement
e.g., NIS2 · DORA · ISO 27001
Discretionary security requirement — Set by risk appetite
Minimal compliance requirement — e.g., NIS2 · DORA · ISO 27001
Continuous threat exposure management
Exposure management that never stops running.
We combine external attack surface management with internal asset context, bringing the attacker’s outside-in view together with what matters inside your business.
The result is a ranked list of exposures based on reachability, business context and potential impact—not technical severity alone. Your IT team knows what to fix first, why it matters and who owns it.
The path is real: internet → controller → nurse workstation → patient records.
- 01 — Scoping
- 02 — Discovery
- 03 — Prioritization
- 04 — Validation
- 05 — Mobilization
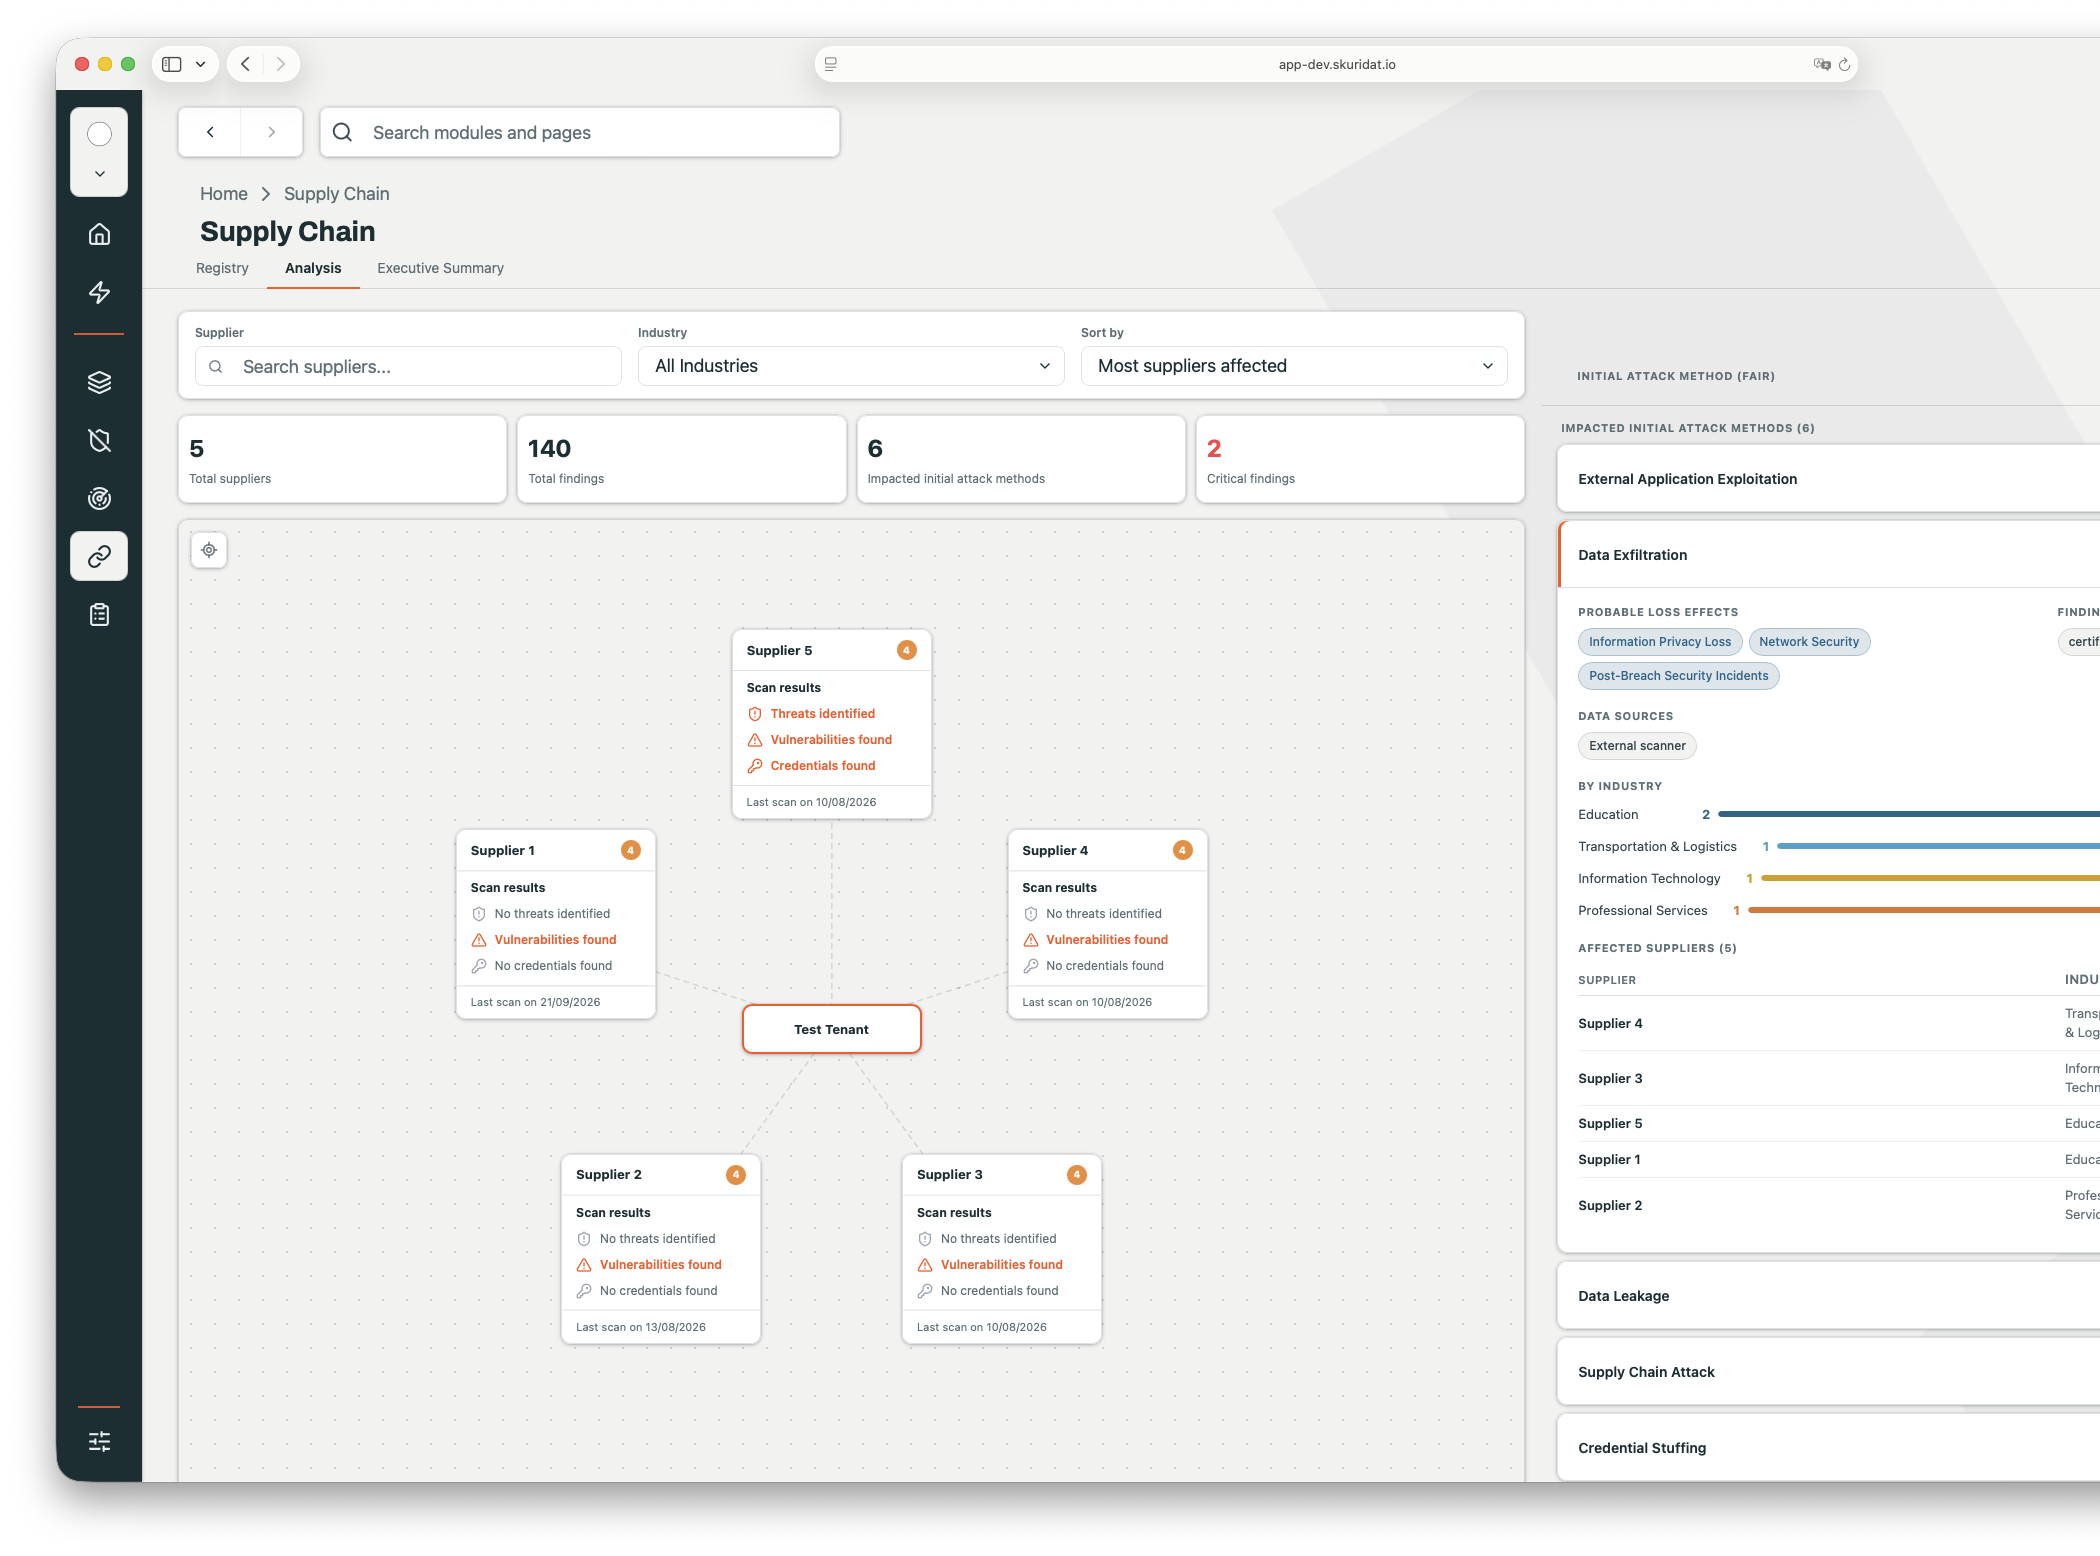
Vendors are not questionnaires.
Suppliers are interconnected parts of your value chain. We continuously observe their external attack surface to identify exposures that could put your operations at risk.
Focus vendor risk management on the suppliers that matter most, and bring observable security evidence into assessments, reviews and renewal decisions.
Operating model
Your risk appetite sets the line.
European SMEs need cybersecurity expertise without building enterprise-sized security teams. Our model combines your IT staff with AI-augmented specialists and on-demand senior expertise: specialists absorb the everyday load, and when a domain pushes past the threshold you've agreed, senior judgment is drawn in — then withdraws once it's back inside.
AI supports analysis and execution; experienced professionals decide where it matters. Not replacing scarce expertise — multiplying its reach.
Your IT team
Fixed. The core never moves.
AI-augmented specialists
Always on — rise and fall with load.
On-demand senior expertise
Drawn in only beyond the threshold.
What changes
Security work you can account for.
Fewer fixes, more risk removed
Effort goes to reachable exposures on critical assets—not an endless CVE backlog.
Compliance evidence as a by-product
NIS2, DORA and ISO 27001 evidence emerges from continuous security work, not an annual scramble.
A budget you can defend
Security spend maps to exposure, business importance and the risk it reduces.
Fewer surprises from suppliers
See external supplier exposures before they become your operational problem.
Senior expertise without the headcount
AI-augmented specialists provide capability you would otherwise have to hire.
Better answers for management
Translate technical exposure into business impact, priorities and remaining risk.
European by architecture
Your cybersecurity stack should not create another supply-chain dependency.
Our platform is built, hosted and operated using European technology and suppliers, keeping security data and critical dependencies within the EU. Digital sovereignty as a design constraint, not a marketing claim.
Built by practitioners.
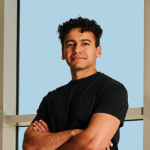
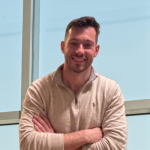
Founded by an ethical hacker and cybersecurity architect with experience spanning offensive security, enterprise architecture, risk and information security.
OSWE · OSCP · CISSP · TOGAF · ISO 27001 · CISM
Where this ends
You started in the dark. You don't have to stay there.
Start with one business service. We map its external exposure, identify what attackers can reach, and turn the findings into a prioritized list of actions—with context, ownership and remediation guidance.
No endless vulnerability report. Just a clear answer to what matters, why, and what to do next.
Prefer to talk first? 20 minutes with a founder →
Two weeks · one business service · EU-hosted, deleted after 30 days
Example extract — external footprint
Static example. Your version is built from your own domains.