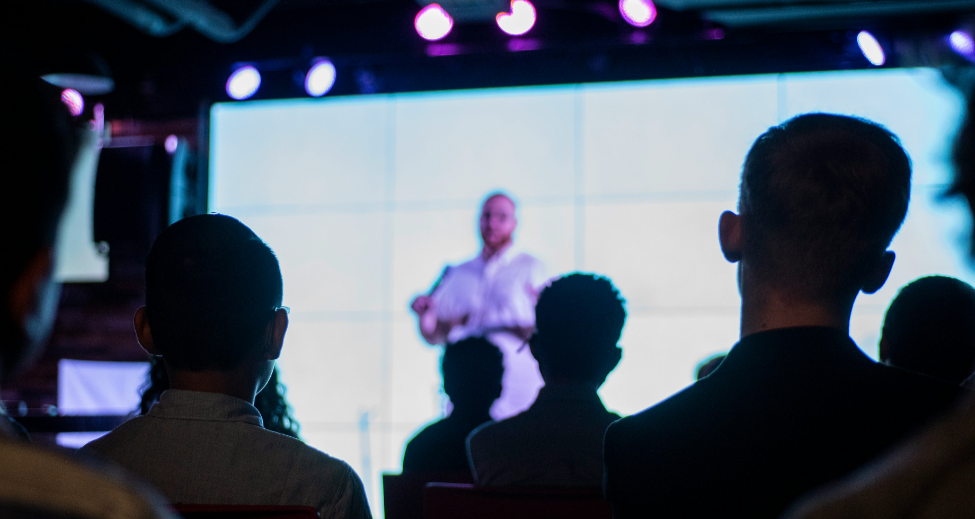
At one of the Netherlands’ largest cybersecurity events this year, Cybersec Netherlands, speakers from government, industry and academia set out the threats and opportunities ahead. The message was consistent: things are shifting fast, and EU regulation together with the rise of AI will decide which organizations keep up.
From over a hundred sessions we distilled six recurring themes. Here is what is noise, what matters, and what each one means for your business.
1. Resilience over prevention
A decade ago the focus was prevention: bigger firewalls, tighter controls. Today the consensus is that no system is unbreakable, and the focus has shifted to resilience, the ability to withstand, respond and recover.
In practice that means testing backups regularly and keeping them offline, running crisis simulations with leadership teams rather than only with IT, and rehearsing assume-breach scenarios.
For Dutch businesses, especially in logistics and manufacturing where a stoppage ripples outward, this is not a slogan. Our take: here to stay.
2. NIS2 will reshape operations
The EU’s NIS2 Directive raises the bar for governance and reporting, with a hard deadline of Q2 2026. Dutch organizations in critical sectors, and their suppliers, must prove they are in control.
This involves more than IT. Boards, legal and compliance teams are all engaged. The key requirements:
- Clear accountability for cybersecurity at management level.
- Mapping and monitoring supply chain dependencies.
- Documenting and reporting major incidents quickly.
Even if your industry is not directly in scope, NIS2 will cascade through contracts, much as GDPR did.
3. OT security moves to the front
Cybersecurity is no longer limited to laptops, servers and cloud apps. The digitization of operational technology, meaning machines, production lines, rail systems and energy grids, gives attackers targets with real-world consequences.
For the Netherlands, with its dense infrastructure, OT security is now a board-level concern. Practical steps: segregate IT and OT networks and keep them apart, use digital twins to baseline the physical estate and monitor for anomalies, and train engineers and operators in cyber hygiene.
If ports or factories go down, the economy takes the hit immediately.
4. AI is both a threat and a tool
AI is no longer hypothetical, and attackers already use it to generate phishing campaigns and voice deepfakes, automate vulnerability scanning and exploit development, and spread disinformation at scale.
Defenders benefit too, but should avoid AI-magic promises and demand proof of effectiveness. For now, businesses should update awareness training for AI-driven scams, evaluate and validate AI-enabled tools carefully, and stay aware that whatever is available to them is also available to attackers.
5. Sovereignty and collaboration
Dutch and European organizations face a balance: reliance on US hyperscalers for cloud and AI against growing regulatory and political pressure for digital sovereignty. Complete independence is unrealistic, but transparency and control in the supply chain are not.
Collaboration is the other half. Whether through Information Sharing and Analysis Centres (ISACs) or initiatives like Dutch Cyber Chain Resilience, businesses are expected to share intelligence and defend together.
6. The human factor remains central
Despite advances in AI and technology, mistakes by employees are still the most common entry point for an attacker.
Dutch businesses should go beyond one-off training. Psychology-based programs, gamification and ongoing reinforcement are becoming the standard, and reducing human error is still one of the most cost-effective measures available.
A checklist for your project calendar
Five priorities for the coming quarters:
- Get NIS2-ready. Governance, documentation and supply chain checks.
- Build resilience. Assume breach, test recovery, rehearse incidents.
- Secure OT environments. Segment networks and train engineers.
- Prepare for AI-driven threats. Train staff, validate AI tools.
- Strengthen collaboration. Join ISACs, share intelligence, insist on transparency.
Written by Sander Rurup, GRC & IT architecture
Cybersecurity consultant with close to a decade of consulting experience in enterprise architecture, information security management and security auditing across regulated European industry. Sander translates exposure into business requirement, governance and ownership.
TOGAF · ISO 27001 · CISM


